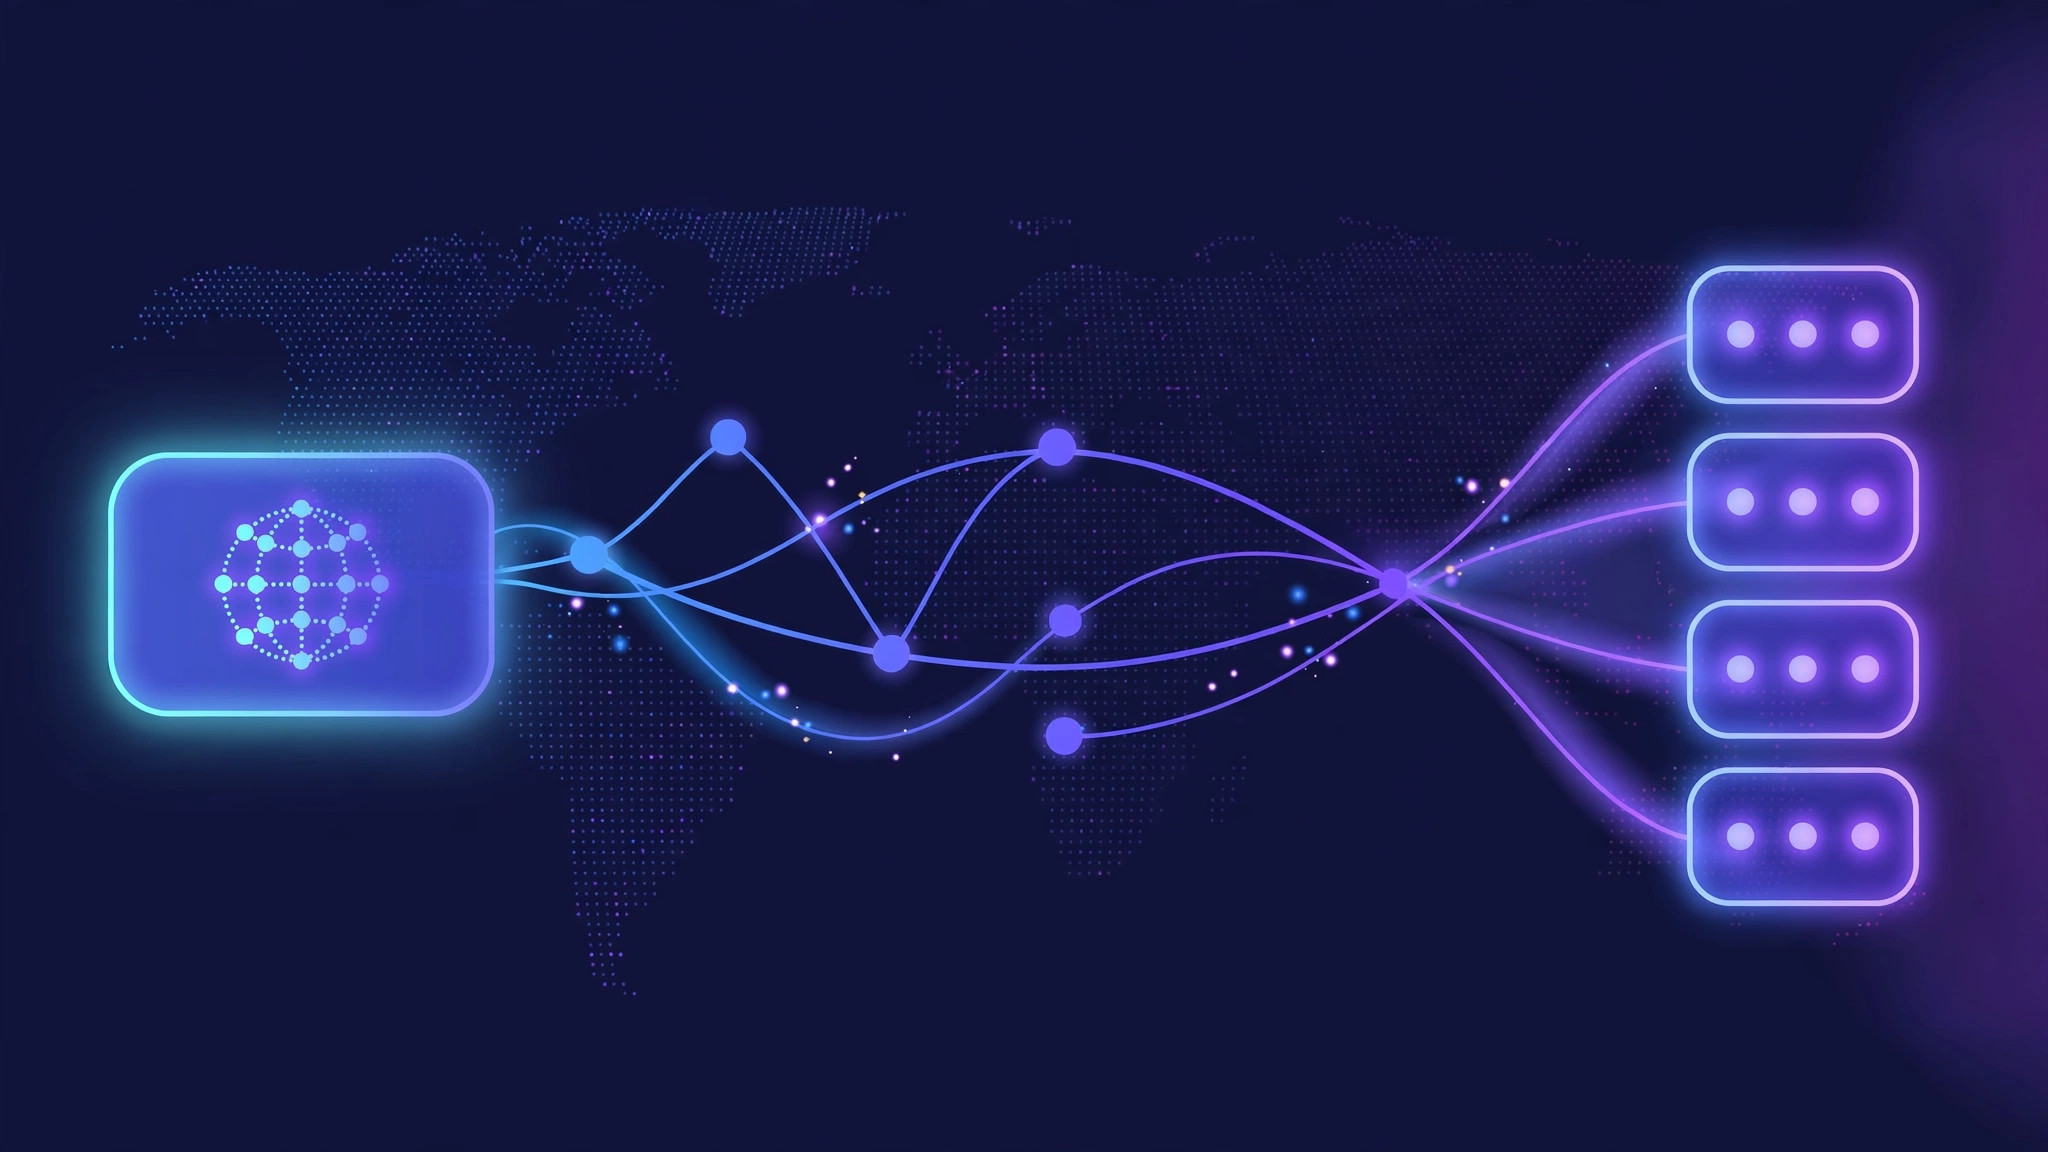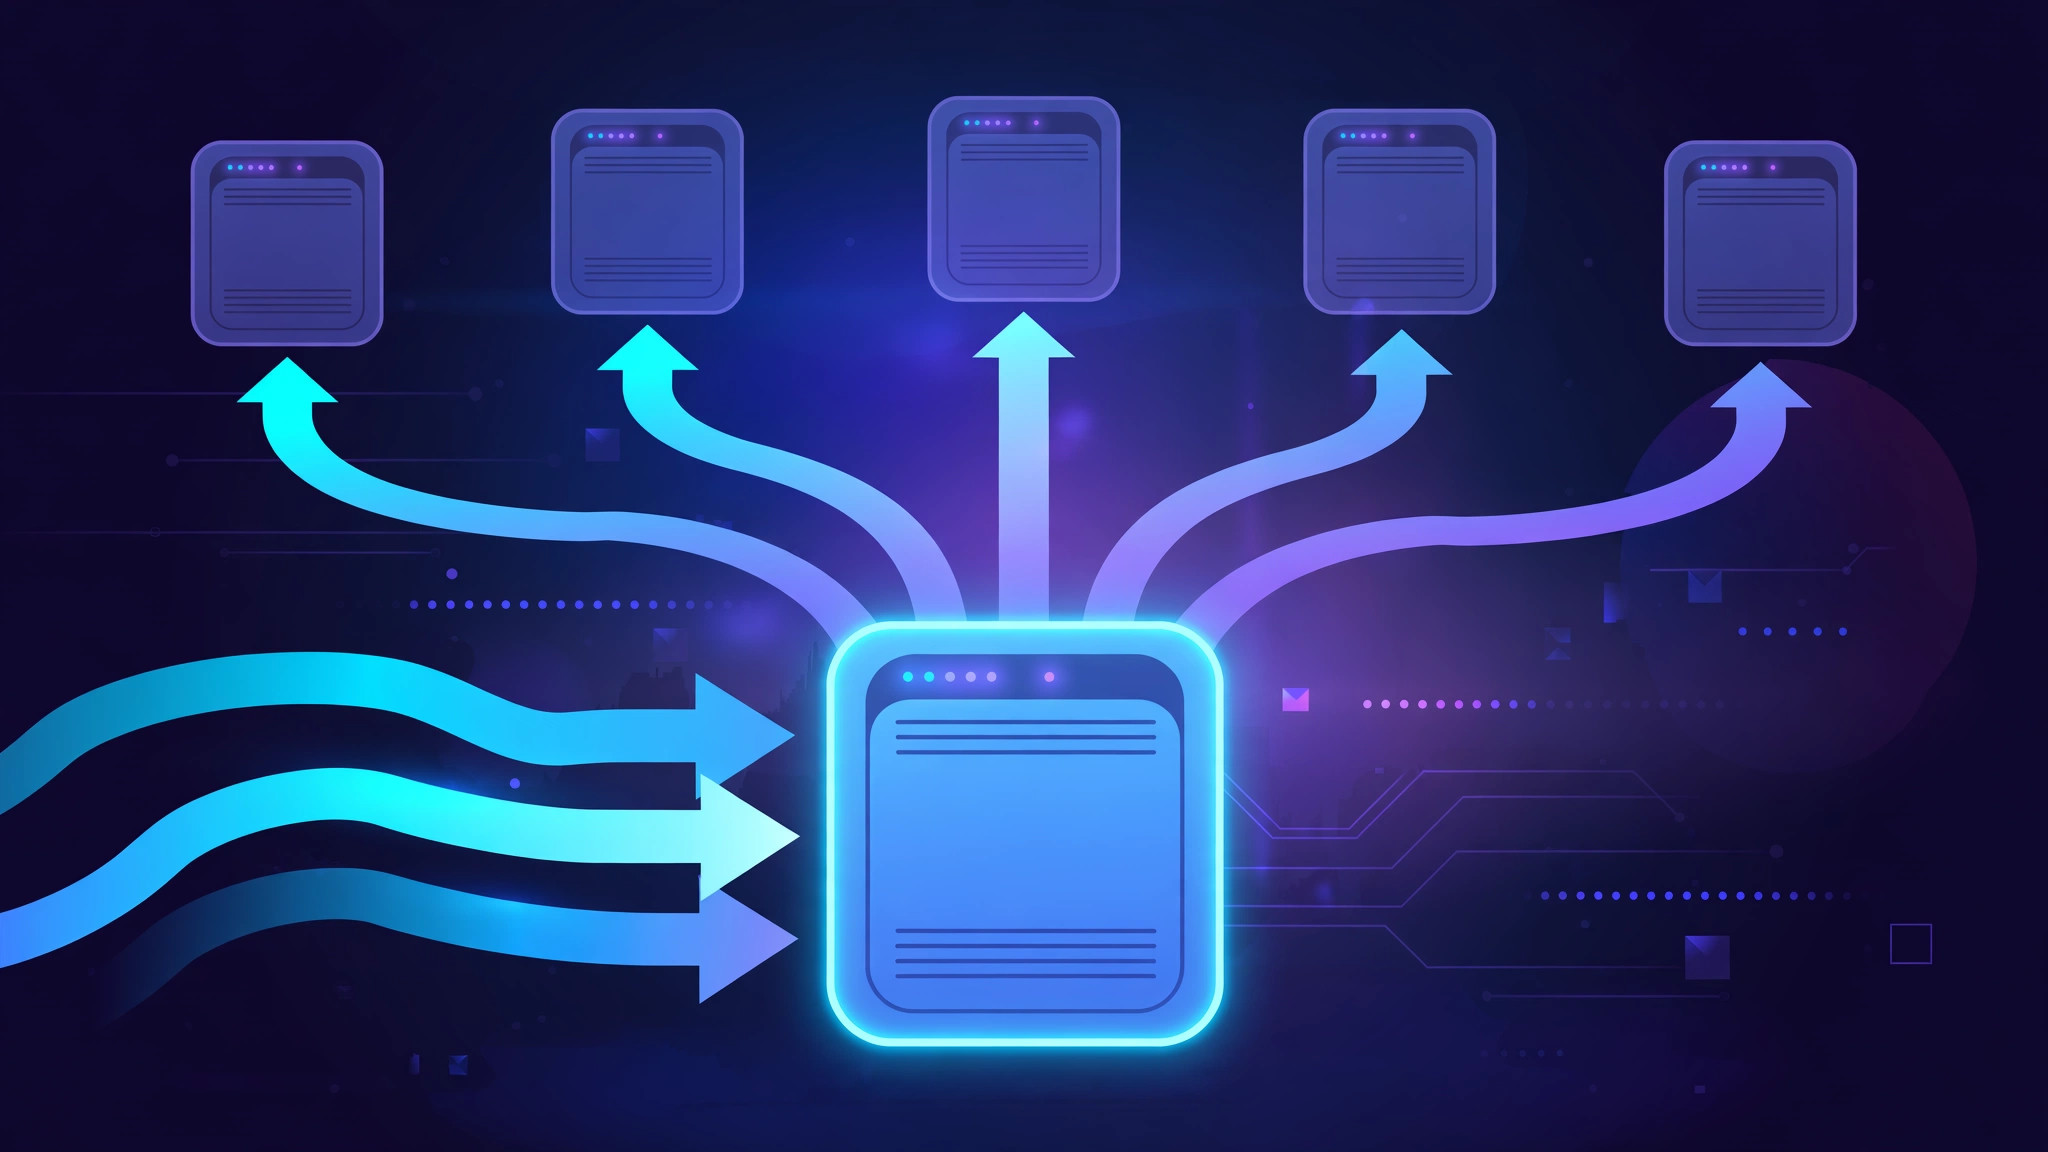
A reverse proxy is a server that sits in front of one or more web servers and intercepts every request from visitors before it reaches your application. Instead of connecting to your app directly, clients only ever talk to the proxy, and the proxy quietly passes each request on to the right backend server.
If you have ever run a serious website, you have probably used one already, possibly without calling it that. Nginx in front of a Node.js app, Cloudflare in front of a WordPress site, a load balancer in front of two application servers: all of these are reverse proxies at work. This guide explains what a reverse proxy actually is, how it handles a request step by step, and when adding one to your setup makes sense.
What is a reverse proxy?
A reverse proxy is a server that accepts incoming requests on behalf of your backend servers and forwards them to whichever backend should handle the job. From the visitor's point of view, there is only one server: the proxy. The real application servers behind it stay invisible.
Think of the front desk of a large office building. Visitors never walk straight into the offices. They check in with the receptionist, who verifies who they are, directs them to the right floor, and handles deliveries and packages at the door. The staff inside can focus on their work, and the building stays secure because there is exactly one controlled entry point. A reverse proxy is that front desk for your servers.
The proxy typically listens on the standard web ports, 80 for HTTP and 443 for HTTPS, using your public domain name and IP address. Your application servers, meanwhile, can run on private addresses and non-standard ports that nobody outside your network can reach.
How a reverse proxy works
Here is what happens, step by step, when someone opens a page on a site that uses a reverse proxy:
- The client sends a request. A visitor types your domain into a browser. DNS resolves that domain to the IP address of the reverse proxy, not to your application server.
- The proxy receives the request. The reverse proxy accepts the connection, reads the request, and checks it against its rules: which domain was requested, which URL path, and sometimes which headers or cookies came with it.
- The proxy picks a backend. Based on those rules, it chooses a backend server. That might mean sending
/blogrequests to a WordPress server and/apirequests to an API server, or spreading identical requests across several app servers in turn. - The proxy forwards the request. It opens a connection to the chosen backend, usually over your private network, and passes the request along, adding headers such as
X-Forwarded-Forso the backend still knows the real visitor's IP address. - The backend responds to the proxy. The application server processes the request and sends the response back to the proxy, never to the visitor directly.
- The proxy returns the response. Before sending it on, the proxy may cache the content, compress it, or add security headers. The visitor receives the page, with no idea a middleman was involved.
The whole exchange adds a tiny hop, but because the proxy and the backends usually sit in the same data center or even on the same machine, the delay is measured in fractions of a millisecond.
Forward proxy vs reverse proxy
The two are easy to confuse because both sit in the middle of a connection. The difference is who they work for:
- Position: A forward proxy sits in front of clients (users and their devices). A reverse proxy sits in front of servers.
- Who it hides: A forward proxy hides the identity of the client making requests. A reverse proxy hides the identity and location of the servers answering them.
- Who sets it up: A forward proxy is configured by the network the users belong to, such as a company or school. A reverse proxy is deployed by the website or application owner.
- Typical jobs: Forward proxies filter outgoing traffic, enforce company internet policies, and cache content for a local network. Reverse proxies balance load, protect backends, and manage incoming web traffic.
- Visibility: Users of a forward proxy usually know it exists because their browser or network is configured to use it. A reverse proxy is completely transparent: visitors cannot tell it is there.
What a reverse proxy is used for
Load balancing
When one server is no longer enough, a reverse proxy spreads incoming requests across several backend servers using methods such as round robin or least connections. It also runs health checks, so if one backend fails, traffic automatically goes to the healthy ones and visitors see no downtime.
Caching
The proxy can store copies of responses, images, CSS, JavaScript, even full pages, and serve them directly without bothering the backend. For busy sites this removes a huge amount of repetitive work from the application servers.
SSL termination
Decrypting HTTPS traffic takes CPU power. A reverse proxy can handle all encryption and decryption in one place, while the backends communicate over plain HTTP inside the private network. It also means one place to install and renew certificates, for example with Let's Encrypt, instead of configuring them on every server.
Security and hiding the backend
Because the proxy is the only machine exposed to the internet, your real servers and their IP addresses stay hidden. Attackers cannot target what they cannot see. The proxy is also the natural place to add rate limiting, block abusive traffic, and filter out malicious requests before they reach your application.
Compression
The proxy can compress responses with gzip or Brotli on the way out, so pages travel smaller and load faster, without changing anything in your application code.
A single entry point for many services
One domain can front many different applications: the main site on one server, an API on another, a blog on a third. The proxy routes each path to the right service, and centralizes logging and monitoring in one place.
A minimal Nginx configuration shows how simple the core idea is:
server {
    listen 80;
    server_name example.com;

    location / {
        proxy_pass http://127.0.0.1:3000;
        proxy_set_header Host $host;
        proxy_set_header X-Forwarded-For $remote_addr;
    }
}
With just this, every request to the domain is forwarded to an application running on port 3000, which itself never needs to be exposed to the internet.
Popular reverse proxies
- Nginx: The most widely used option. It started as a web server and is now the default reverse proxy and load balancer for a huge share of the web, valued for its speed and low memory use.
- HAProxy: A dedicated, high-performance load balancer and reverse proxy, especially strong for very high traffic and detailed health checking and statistics.
- Apache mod_proxy: If your stack already runs on the Apache HTTP Server, its built-in proxy modules can reverse-proxy to HTTP and other backends without adding new software.
- Cloudflare: A cloud-based reverse proxy combined with a CDN and DDoS protection. You point your DNS at Cloudflare and it proxies your traffic, so you get many reverse proxy benefits without running a proxy server yourself.
- Traefik: A modern proxy built for containers and microservices. It discovers Docker and Kubernetes services automatically and can fetch Let's Encrypt certificates on its own.
When should you use one?
A reverse proxy earns its place when any of the following become true: your traffic is outgrowing a single server, you run more than one application or service under one domain, you want HTTPS certificates managed in one place, or your backend should not be directly reachable from the internet. Most growing production websites check at least one of these boxes.
It is also worth knowing the limitations:
- Single point of failure: If the proxy goes down, everything behind it goes down. Serious setups run two proxies with a failover mechanism.
- Extra complexity: It is one more component to configure and maintain. A wrong setting, such as a missing forwarded header, can break IP-based logging or features until it is fixed.
- Not always necessary: A tiny personal site on a single server works fine without one. The benefits show up as traffic, services, and security needs grow.
Conclusion
A reverse proxy is the controlled front door of your infrastructure: it receives every request, decides which backend should answer, protects and accelerates the exchange, and keeps your real servers out of sight. Once a website grows beyond a single box, it stops being an optional extra and becomes standard practice.
XpertBees helps businesses set up and manage servers and web infrastructure, including Nginx reverse proxies, load balancing, and SSL, so your applications stay fast, secure, and online.