DNS, short for Domain Name System, is the system that translates human-friendly domain names like xpertbees.in into the numeric IP addresses computers use to find each other on the internet. It is often called the internet's phonebook: you remember the name, and DNS looks up the number. Every time you open a website, send an email, or use an app, a DNS lookup happens quietly in the background, usually in a fraction of a second.
Why DNS exists
Computers do not locate each other by name. They communicate using IP addresses, strings of numbers such as 192.0.2.1 for IPv4 or longer IPv6 addresses such as 2001:db8::1. A single website may sit behind several IP addresses, and those addresses can change when a server moves, a hosting provider migrates its infrastructure, or a content delivery network reroutes traffic.
Names solve the human side of the problem. Nobody could remember the IP address of every site they visit, and businesses could never change hosting providers if every customer had memorized a number. DNS separates the stable public name from the changeable technical address. When the address behind a name changes, only the DNS record changes; visitors keep typing the same domain.
DNS is also distributed rather than centralised. There is no single master list of every domain on the internet. Responsibility is delegated in a hierarchy, from the root of the system down to individual domain owners, which lets DNS scale to billions of lookups a day without a central bottleneck or a single point of failure.
How DNS works: the lookup journey
When you type a domain into your browser and press Enter, a chain of lookups runs before the page can load. In practice it takes milliseconds, because caching short-circuits most of it. Here is the full journey, step by step:
- Browser cache. Your browser first checks its own memory. If you visited the site recently, it may already know the IP address and skip the lookup entirely.
- Operating system and local cache. If the browser does not know, it asks the operating system, which checks its own cache and the local hosts file, a small manual name-to-address mapping some systems keep for fixed entries.
- Recursive resolver. Still no answer? The query goes to a recursive resolver, usually run by your internet provider or a public service such as Google Public DNS (8.8.8.8) or Cloudflare (1.1.1.1). The resolver's job is to track down the answer on your behalf.
- Root nameserver. The resolver starts at the top of the hierarchy. Root nameservers do not know where xpertbees.in is hosted, but they know which servers handle the .in extension, and they point the resolver there.
- TLD nameserver. The resolver then asks the top-level domain (TLD) nameserver for .in. It does not hold the final address either, but it knows which nameservers are authoritative for this specific domain.
- Authoritative nameserver. Finally, the resolver asks the domain's authoritative nameserver, the server that stores the domain's actual DNS records. It returns the IP address held in the domain's A or AAAA record.
- Answer back, then connection. The resolver passes the address to your browser and caches it for a set period, so the next person who asks gets an instant answer. Your browser connects to that IP address, and the page loads.
Because of caching at the browser, operating system, and resolver levels, most lookups never travel the full chain. A popular website's address is usually answered from a nearby cache in a few milliseconds.
Common DNS record types
A domain's DNS zone is a collection of records, and each record type has a specific job. These are the ones you will meet most often:
- A record maps a domain to an IPv4 address. Example: xpertbees.in has an A record pointing to 203.0.113.10, which tells browsers where the website is hosted.
- AAAA record is the IPv6 equivalent of an A record. Example: the same domain can also point to an IPv6 address such as 2001:db8::10 for visitors on IPv6 networks.
- CNAME record points one name to another name instead of an address. Example: www.xpertbees.in is set as a CNAME of xpertbees.in, so both names serve the same website.
- MX record tells the internet which mail servers accept email for the domain. Example: an MX record with priority 10 directs incoming mail to the domain's primary mail server.
- TXT record stores plain text information. Example: businesses use TXT records to prove domain ownership and to publish email security policies such as SPF and DKIM.
- NS record lists the authoritative nameservers for the domain. Example: an NS record tells every resolver which servers hold the official records for that domain.
A single A record, as it might appear in a zone file, looks like this:
xpertbees.in. 3600 IN A 203.0.113.10Reading left to right: the name, the TTL in seconds (explained below), the class (IN stands for internet), the record type, and the value.
DNS propagation and TTL
Every DNS record carries a TTL, short for Time to Live, measured in seconds. TTL tells resolvers and browsers how long they may cache a record before they must ask again. A TTL of 3600 means the answer can be reused for one hour; a TTL of 300 means five minutes.
TTL is exactly why DNS changes do not take effect everywhere at once. When you edit a record, resolvers around the world keep serving the old cached answer until their copy expires. This gradual, worldwide refresh is called propagation. Most changes settle within a few hours, but a long TTL can stretch full propagation to 24 or even 48 hours in the worst cases.
A practical tip follows from this: if you are planning a server migration, lower the TTL on the key records a day or two in advance. Shorter TTLs make caches expire faster, so when you switch the record to the new server, visitors are directed to it sooner and the old server can be retired with far less risk of stragglers landing on it.
DNS and website speed and security
DNS affects performance more than most people realise. Before a browser can request a single file from your website, it needs the IP address, so a slow resolver or a lookup that misses every cache adds delay to the first visit. Fast resolvers, sensible TTLs, and well-distributed nameservers all shave milliseconds off page loads.
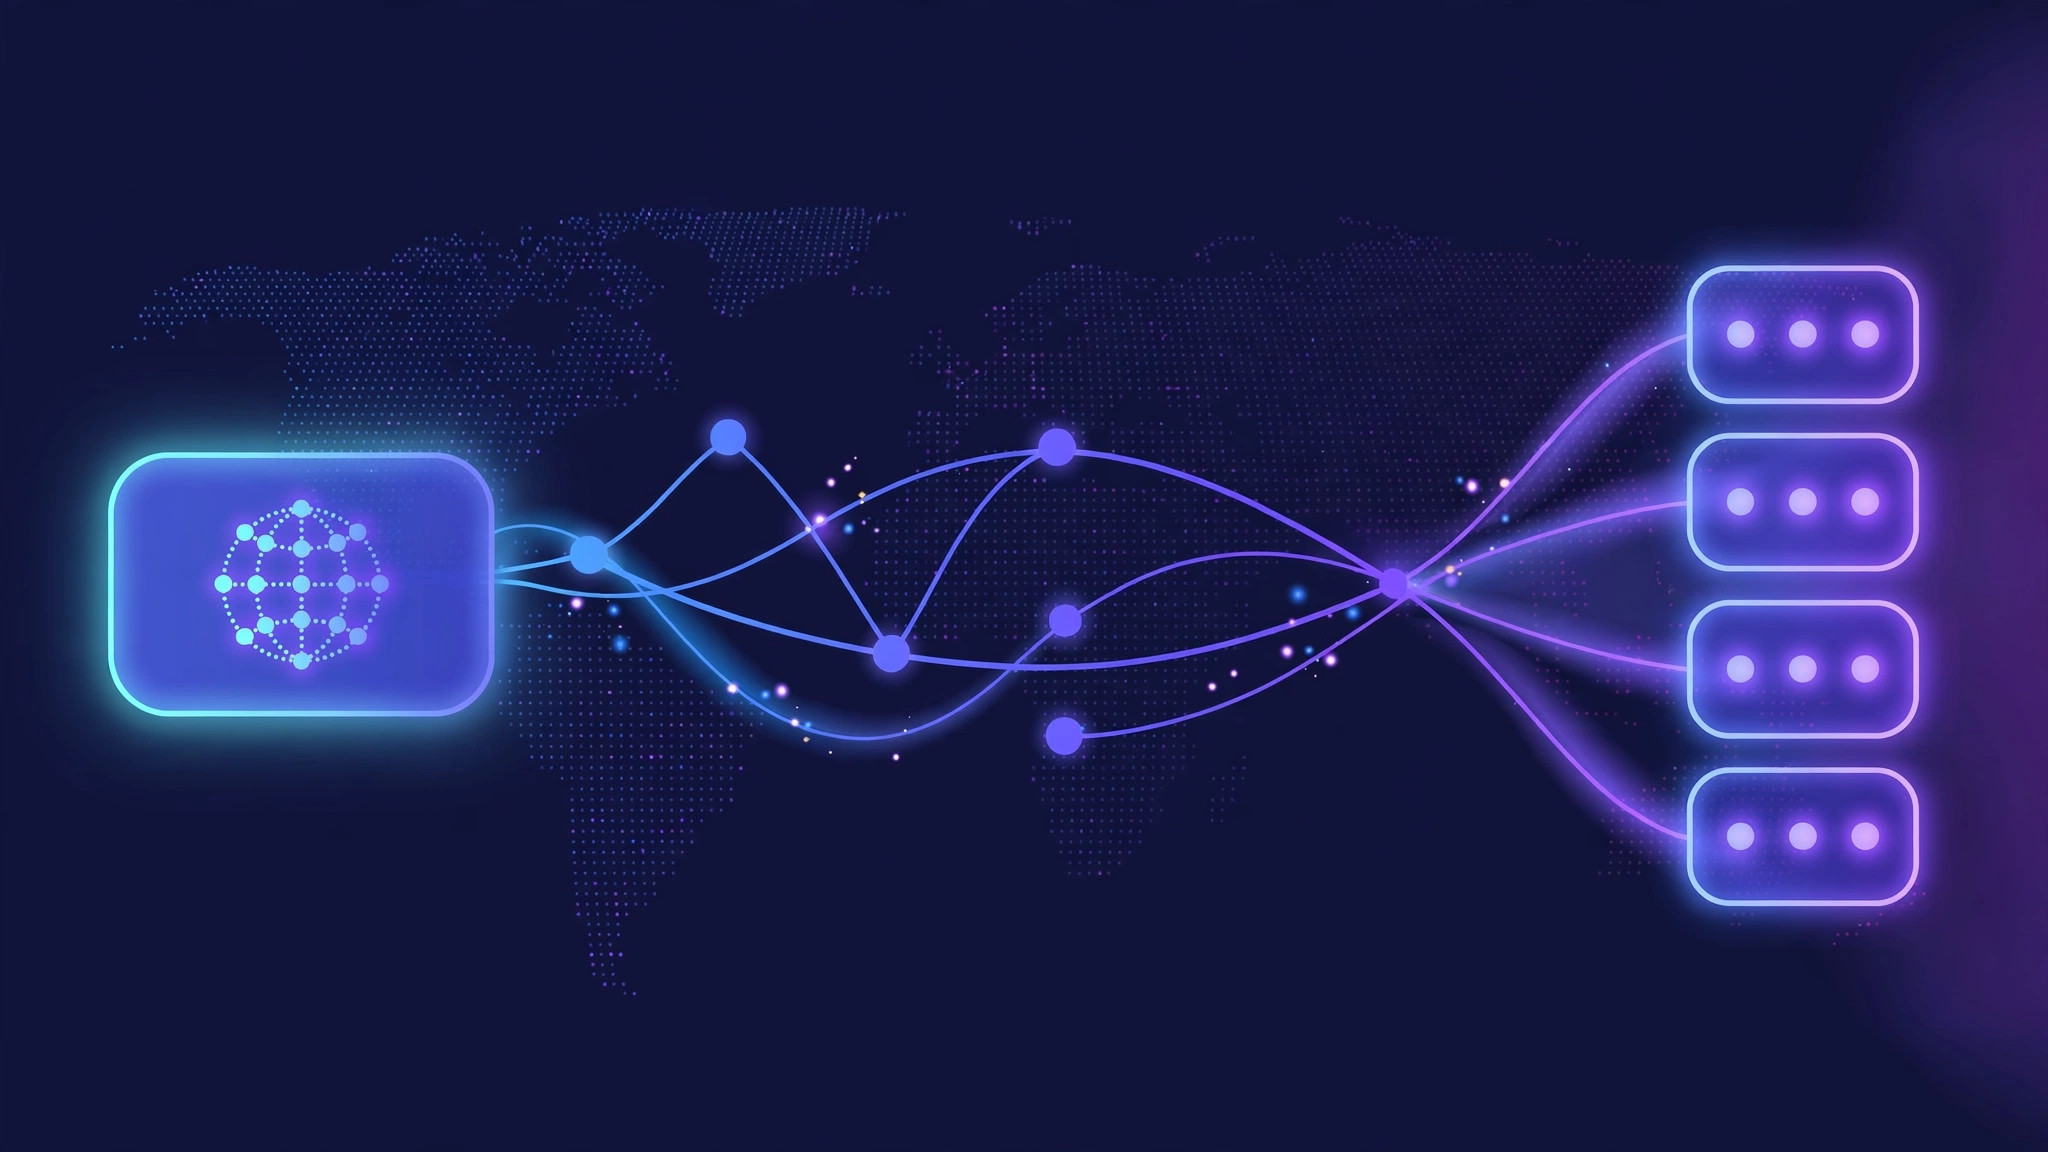
Many DNS providers use anycast, a routing approach where the same nameserver address is announced from many locations worldwide. A visitor's query is answered by the nearest healthy server, which improves both speed and reliability: if one location fails, queries automatically flow to the next nearest one.
On the security side, traditional DNS queries travel in plain text, so networks along the path can see which domains a user looks up. DNS over HTTPS (DoH) encrypts those queries inside ordinary HTTPS traffic, which improves privacy and makes tampering harder. Separately, DNSSEC adds digital signatures to DNS records, so resolvers can verify that an answer genuinely came from the domain's authoritative server and was not forged on the way.
Common DNS problems
When a website or email service misbehaves, DNS is a frequent suspect. These are the problems we see most often, and what each one actually means:
- Propagation delay. You changed a record and some visitors still reach the old server. This is usually normal caching behaviour, not an error. Confirm the new value is spreading with an online DNS lookup tool, then wait for old caches to expire.
- Wrong or missing records. A typo in an IP address, a deleted A record, or an MX record pointing at the wrong host will break the website or email for everyone. Always double-check record values against your hosting details before saving changes.
- NXDOMAIN errors. The browser reports that the domain does not exist. This happens when the domain registration has expired, the name was typed incorrectly, or the domain genuinely has no records published. Check the registration status and spelling first.
- Stale local cache. Everyone else sees the updated site except you. Your computer, browser, or router is holding an old answer. Restarting the browser, flushing the operating system's DNS cache, or temporarily switching to a public resolver usually clears it.
Conclusion
DNS is the quiet translation layer that makes the web usable: names for people, numbers for machines, and a global hierarchy of caches and nameservers connecting the two. Once you understand how lookups, record types, and TTL fit together, most "the website is down" mysteries turn into quick, methodical checks instead of guesswork.
If your business needs help with hosting, domains, or server management, XpertBees handles the technical side end to end, from DNS configuration and migrations to keeping your servers fast, secure, and online.